Requirements lose context
Generic checklists rarely preserve the exact source, interpretation, version and accountable reviewer behind an obligation.
Guided product demonstration
Follow MBank, our fictional demonstration organisation, from initial profile and risk assessment through evidence, remediation and management-ready assurance.
MBank contains demonstration data only. Teteza360 supports accountable decisions; it does not declare an organisation legally compliant.
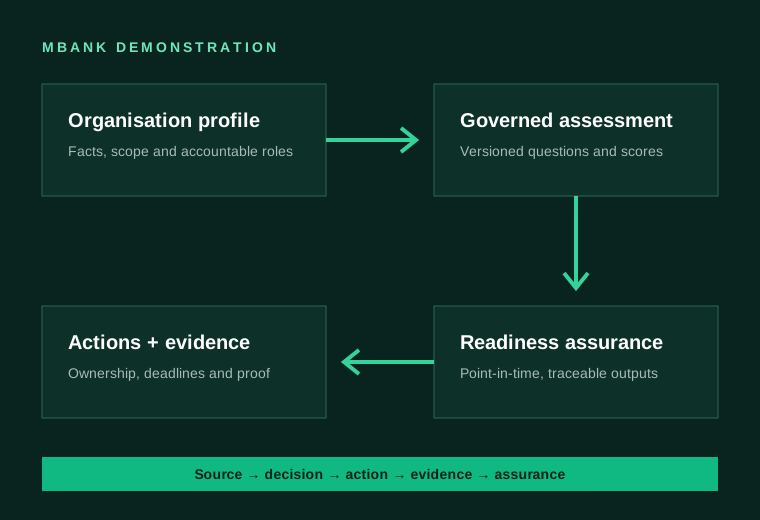
The operating gap
Generic checklists rarely preserve the exact source, interpretation, version and accountable reviewer behind an obligation.
Findings in documents and spreadsheets become difficult to assign, evidence, independently review and close consistently.
Leadership and reviewers need a point-in-time view of risk and evidence—not a manually assembled report whose inputs cannot be traced.
MBank demonstration journey
Configure MBank’s profile, branches, departments, memberships and action-based roles.
Show: Profile, Structure, PeopleComplete a governed assessment whose questions, scoring and legal/control mappings were independently published.
Show: Profiler, AssessmentsCreate action plans, assign corrective actions and preserve comments and approvals.
Show: Action plansUpload private evidence, record classification and validity, map it to controls, and submit it for independent review.
Show: Evidence vaultMaintain processing records, DPIAs, incidents, rights requests, vendors, transfers, training and compliance attention.
Show: Operational workspacesGenerate immutable report snapshots and share selected outputs through a scoped, expiring audit room.
Show: Reports, Assurance ledgerImplemented capabilities
Organisation profile, branches, departments, people, roles, MFA and access reviews.
Governed assessments, findings, action plans, evidence and deterministic scores.
ROPA, DPIAs, privacy notices, consent preferences and rights requests.
Incident response, vendors, cross-border transfers, DPO work and security controls.
Training, registration readiness, regulatory updates, policies and compliance inbox.
Point-in-time reports, controlled audit rooms, audit ledger and governed tenant lifecycle.
Next step
ITES will tailor the journey to your sector, governance model, priorities and evidence landscape.